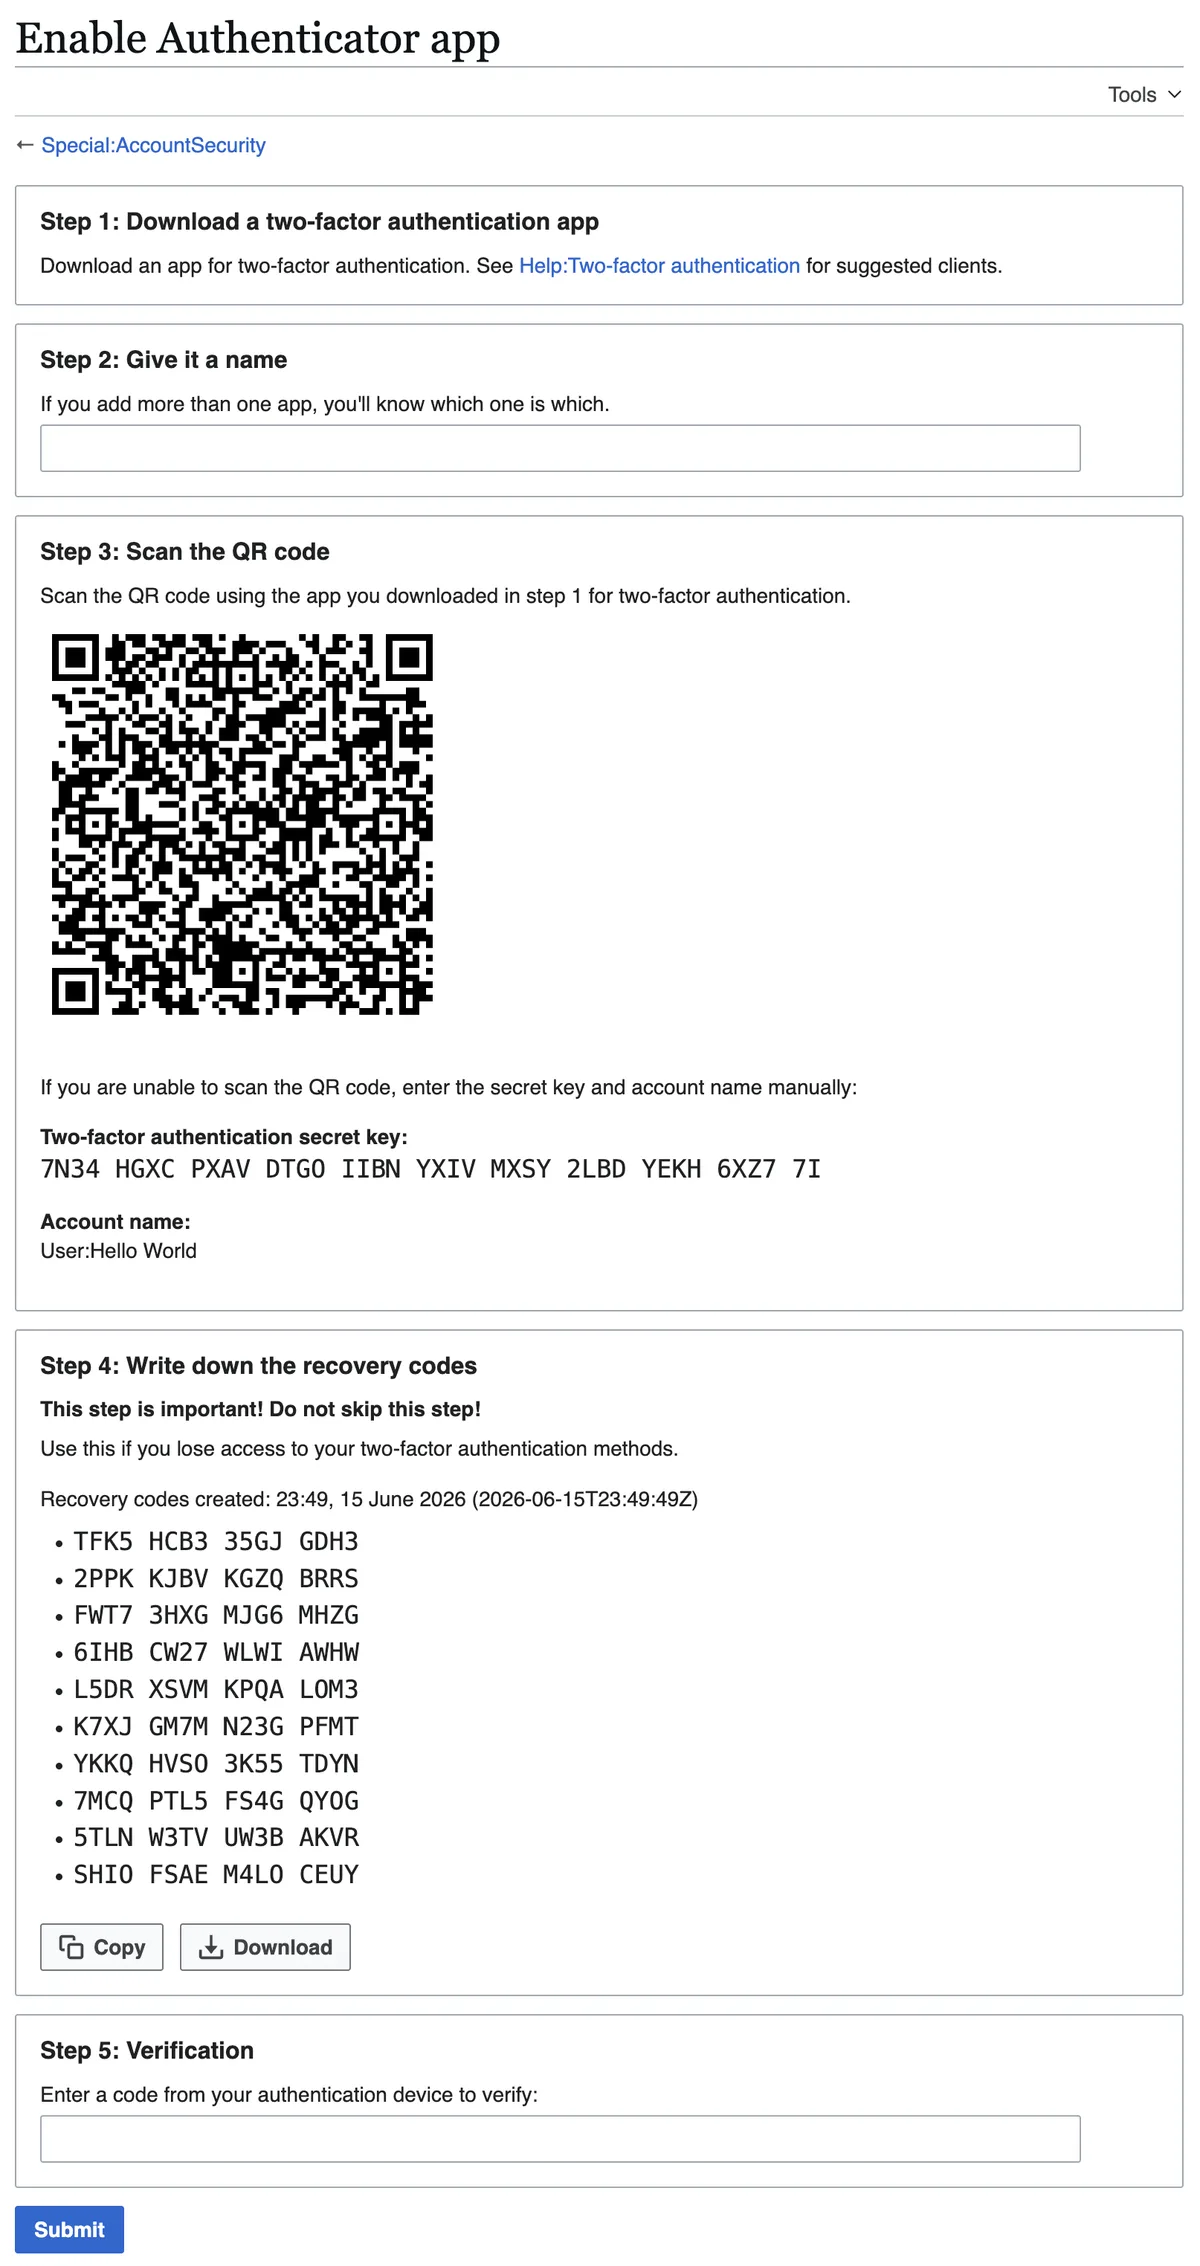
Two-factor authentication in finance apps works best when the second factor is something a phisher cannot simply ask for and receive. An authenticator app, a hardware security key or a passkey meets that standard; a text-message code does not, because it can be intercepted through SIM-swap fraud. The practical hierarchy, from weakest to strongest, runs SMS, authenticator app, security key, with passkeys now emerging as the password-replacing option major platforms are rolling out.
For compliance and legal-ops teams, the distinction is not academic. Authentication method shapes phishing exposure, incident narratives and the controls examiners and insurers ask about. A finance app that offers only SMS codes is carrying a known weakness into every customer session, and the record of that choice is written into its vendor and control documentation. We covered a connected angle in App-Store Review Guidelines for Regulated Finance Features: Compliance When the Platform Is a Regulator Too.
This explainer sets out how the methods differ, why some resist phishing and others do not, and what the operational consequences are for teams governing mobile finance products. It sits alongside broader coverage of Banking App Permissions: What Users Grant, Risks That Follow and the Apps desk.
What is two-factor authentication, in plain terms?
Two-factor authentication is a login check that asks for proof from two different categories rather than one. As NYT Wirecutter explains in its guide to authentication apps, the three categories are something you know, such as a password or PIN; something you have, such as a phone or a security key; and something physically unique to you, such as a fingerprint or face scan.
A password alone is one factor. If an attacker steals or phishes it, the account falls. Adding a second factor from a different category raises the bar, because the attacker now also needs the user's phone, key or biometric. Wirecutter's assessment is blunt: years of breaches have shown passwords alone are not enough, and enabling 2FA is the best way to keep online accounts secure.
The definition matters for governance documents too. A control described as "multi-factor authentication" in a policy should say which factors it actually combines, because "password plus SMS code" and "password plus hardware key" are very different controls wearing the same label.
Why are text-message codes the weakest option?
SMS codes are the most common implementation and the least secure, per Wirecutter, because a clever attacker can use a SIM swap to intercept codes sent by text. A SIM swap is fraud in which someone convinces or tricks a mobile carrier into moving a victim's phone number to a device the attacker holds; the codes then arrive on the attacker's phone, not the user's.
Wirecutter's guidance is calibrated rather than absolute: any 2FA beats no 2FA, so a user whose only workable option is SMS should keep using it, while understanding the risk. The same reasoning applies to product teams. Offering SMS as a fallback is defensible; offering it as the only method is a choice that should be documented and justified.
Android-focused guidance reaches the same conclusion from the user side. As Talk Android advises in its checklist for securing payment and finance apps on Android, text-message codes are better than nothing but can be intercepted through SIM-swap fraud, and users should prefer an authenticator app or a hardware security key where the choice exists.
What do authenticator apps and security keys actually do?
Authenticator apps generate a short numeric code on the user's own phone, on a timer. Wirecutter notes two properties that make them stronger than SMS: they work without a data connection, and the codes are generated on the device, so they cannot be intercepted in transit. They are also free and widely supported, which is why they are the default recommendation for most users.
Hardware security keys, such as plug-in or tap tokens, are the strongest form per Wirecutter. They are resistant to phishing attacks, meaning a fake login page cannot harvest a usable credential from them. The trade-offs are cost and limited site support, which is why Wirecutter reserves its strongest caution for higher-risk individuals, such as politicians, activists and journalists, who should use phishing-resistant options wherever possible.
There is a residual weakness even with authenticator apps. Wirecutter observes that a user of any 2FA app can still be tricked into entering a code on a phishing site, and that attackers' techniques keep improving. The app raises the cost of an attack; it does not make the user immune to social engineering. That is why staff training and login-page hygiene remain controls in their own right.
Where do passkeys fit, and are they ready?
Passkeys are a newer credential type intended to replace passwords and 2FA with phishing-resistant credentials stored on the user's device. Wirecutter describes them as backed by Apple, Google and Microsoft, and notes the practical catch: passkeys are still new, so users who adopt them still need authenticator apps for the many sites that do not yet support them.
Talk Android reports that major apps are now rolling out passkey support, naming WhatsApp as an example, and that setting one up is easier than it used to be. For a finance app product owner, the planning consequence is a transition period in which passkeys, authenticator apps and SMS all coexist, and the enrollment flows and fallback logic for all three must be maintained at once.
For governance, passkeys change the recovery question. A lost passkey is a device-bound credential problem, not a password reset problem, and the account-recovery path becomes the weakest link. Recovery flows deserve the same design scrutiny as the login flow itself.
What do examiners, insurers and app platforms expect?
The retrieved material does not document specific examiner requirements or insurer mandates, so this section stays within what it supports. Two expectations are visible in the record. First, the security press treats phishing-resistant second factors as the standard a careful user should meet: Talk Android's checklist directs users of payment and finance apps toward authenticator apps, hardware keys and passkeys, and away from SMS where possible. Second, Wirecutter frames 2FA as the baseline control for any account protected by a password, not an optional extra.
Read across adjacent compliance obligations, the pattern is consistent. Regulated finance apps already answer for their permission footprint, their update lifecycle and their disclosure design; authentication strength is the same kind of documented, testable control. A team that can state which factors it supports, which it defaults to, and how it handles recovery has an answer ready. A team that cannot, does not.
Practical steps for a compliance or legal-ops team reviewing a finance app's authentication posture:
- Inventory the second factors each app supports, and record which is the default at enrollment.
- Flag any app where SMS is the only option, and document the rationale or the remediation plan.
- Review the account-recovery path with the same rigor as login, since recovery is the bypass attackers use.
- Track passkey support across the app portfolio, and plan the coexistence period rather than discovering it in production.
- Align the policy language with reality, so "multi-factor authentication" in a control document names the actual factors.
What this means in practice
The evidence establishes a clear ordering and a clear transition. SMS codes are the weakest common method, vulnerable to SIM-swap interception. Authenticator apps are free, offline-capable and widely supported, and they remove interception from the threat model while leaving phishing of the code entry itself. Hardware security keys resist phishing outright but cost more and support fewer sites. Passkeys aim to replace the password-plus-code pattern entirely, with backing from the major platform vendors and adoption now visible in major consumer apps.
What remains unresolved is pace. Wirecutter notes that passkey support is incomplete across the web, and Talk Android's checklist is written for a present in which passwords, codes and keys all still coexist. For finance apps, that means the near-term work is not a single migration but a managed mix: push phishing-resistant options where the platform allows, keep a documented fallback, and treat the recovery path as part of the control, not an exception to it.